A secure redirect service.From the certificate to the audit trail.
Every domain you point at RedirHub gets a free HTTPS certificate, bot filtering and DDoS protection at 130 Global PoPs. Every change to a link is recorded with who made it and where it came from. Nothing to install, no certificates to renew.
14-day free trial on Pro. Core starts right away.
Trusted by teams that run links on their own domains
- Global PoPs
- 130
- median first byte. Bitly: 112ms*
- 17ms
- platform uptime
- 99.99%
* From our public redirect speed test: median time to first byte over the last 7 days, averaged over Washington, D.C., Frankfurt and Tokyo. See the provider rankings · Uptime status page
HTTPS
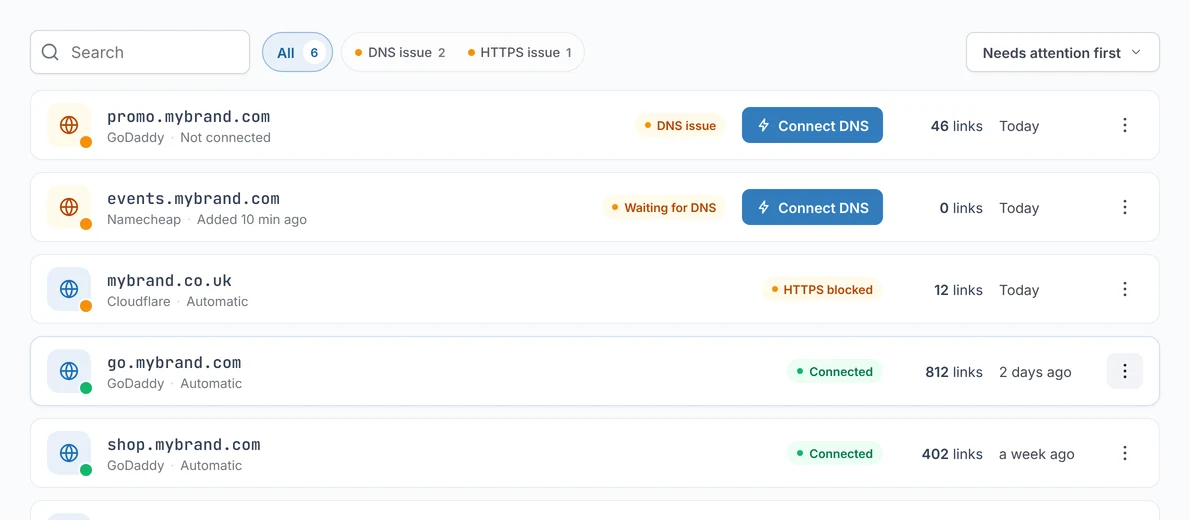
An HTTPS redirect service that issues the certificate for you, and says why when it can't
Point a domain at RedirHub and the certificate is issued as soon as DNS is in place, then renewed before it expires. If something upstream blocks it, the dashboard and your email say exactly what: a DNS proxy, DNSSEC, or a rejected order. No retry loops, no “Not Secure” surprises.
- Free certificate, issued once DNS points to RedirHub. A root domain covers its www variant in the same domain slot. Core Pro Enterprise
- Clear reasons, not endless retries. A blocked certificate is retried on a schedule by error class, and immediately after a DNS change.
- Connect DNS in one step. Automatic setup through Domain Connect at Cloudflare, or manual CNAME / A records with a live check for any other provider.
- Bring your own certificate when a policy requires it. Enterprise

Certificate status, as shown on each hostname
- HTTPS activeIssued and renewed automatically. Nothing to do.
- Pending DNSWaiting for the CNAME or A record. Issued the moment DNS resolves to RedirHub.
- Blocked · proxiedA DNS proxy sits in front of the hostname. Switch the record to DNS only.
- Blocked · DNSSECThe zone's DNSSEC chain fails validation, so the certificate authority can't verify the domain.
- Blocked · rejectedThe certificate authority declined the order. The message tells you what it objected to.
Edge protection
Bots filtered and DDoS absorbed at the edge, on every plan
Malicious crawlers blocked
Filtered at the edge, before they reach your redirect logic or your statistics. Search engines such as Googlebot pass, so your 301s keep being crawled.
DDoS absorbed
Distributed attacks are taken at the 130 PoPs, not at your origin, with no rule for you to write. Redirects keep answering under load.
Analytics count people
The Humans only switch leaves bot clicks out of every figure, and the API and MCP server return a bot-free count next to the total. Errors (4xx and 5xx) are a KPI of their own.

Humans only leaves bot clicks out of every figure on the Analytics page. Click counts in the Links list include bots.
How it's built
Three separate layers, so one problem doesn't take your redirects down
RedirHub runs on AWS as a control plane, a global edge network and an analytics pipeline. Each edge PoP serves redirects from its own copy of the configuration, so the dashboard being updated, or a PoP failing, never stops a visitor being redirected.
Where you make changes
Dashboard, Management API, Terraform provider and the MCP server. Every write is authenticated per user or per workspace-scoped token and recorded in the link's history.
130 Global PoPs, each with its own copy
Redirects, certificates, bot filtering and DDoS protection are served at the PoP nearest the visitor. If a PoP fails, its traffic moves to other PoPs automatically.
Records what happened
Visits, errors and destination health flow into a separate pipeline. A slow report never slows a redirect, and monitoring tells you before your visitors do.
Who changed what
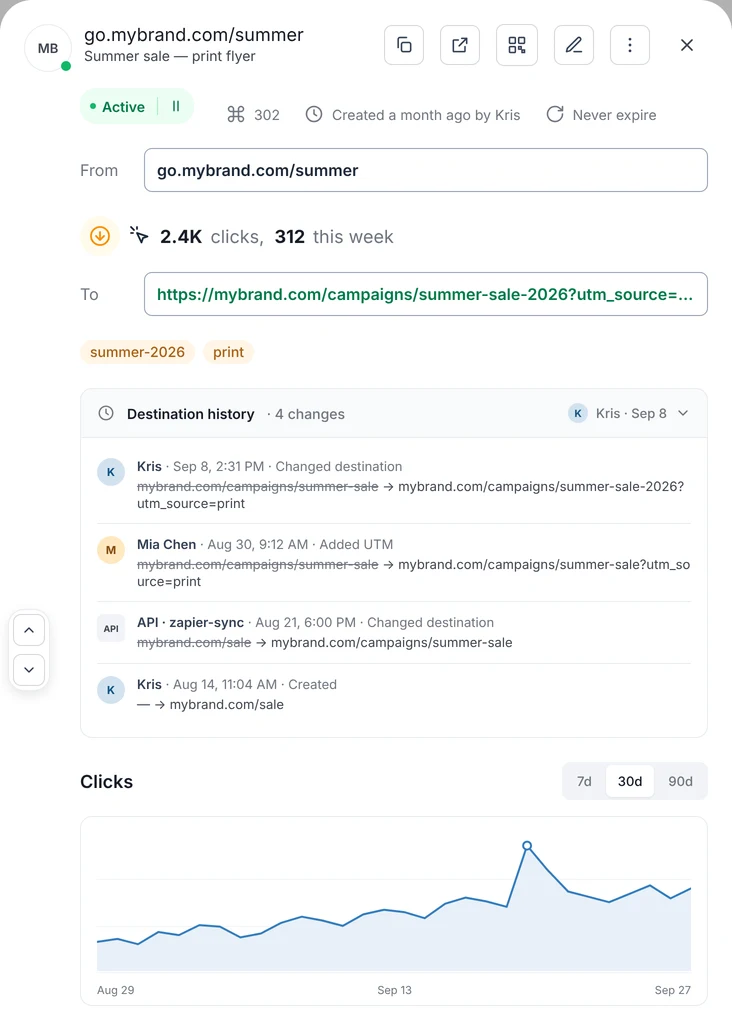
Every change on record: who, when, what it was before, and where it came from
A redirect that silently changed destination is a security incident waiting to be noticed. On RedirHub each link keeps its own history, and each link can carry a private note that says why it exists, so the next person doesn't have to guess.
Change history on every linkPro
Who changed it, when, the old and new value, and whether it came from the dashboard, the API, MCP, a CSV import or Auto-redirect. Shown in the link drawer and readable through MCP.
Workspace audit logPro
One log across the workspace of destination, UTM, redirect type, status and password changes, with filters, a 5-week activity heatmap and CSV export. History is kept for as long as a link exists.
Private notesAll plans
Up to 2,000 characters on each link saying what it is for. Set from the dashboard, the API or an AI assistant, and every change to the note is kept in the history.
Access
Access that is individual, scoped and revocable
No shared logins. Each person signs in as themselves, with two-factor authentication and a list of their own sessions. Each API token belongs to one workspace and expires. Each member has one role.
Every account, properly locked
- Two-factor authentication. A 6-digit code from any authenticator app at each sign-in, with recovery codes that can be shown again or regenerated.
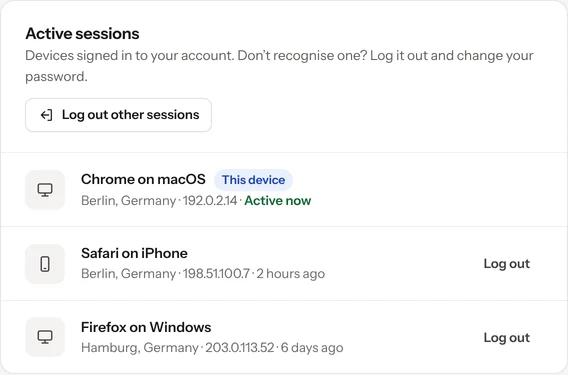
- Sessions you can see. The browsers signed in to the account, with device, browser, location and last activity, and one button to log the others out.
- Google sign-in. Members whose Google account uses the same email sign in with one click. It is a login option, not single sign-on.
- Single sign-on (SAML). Sign in through your identity provider; when someone leaves the directory, their access goes with it. Pro add-on Enterprise · by contract
Automation gets its own keys
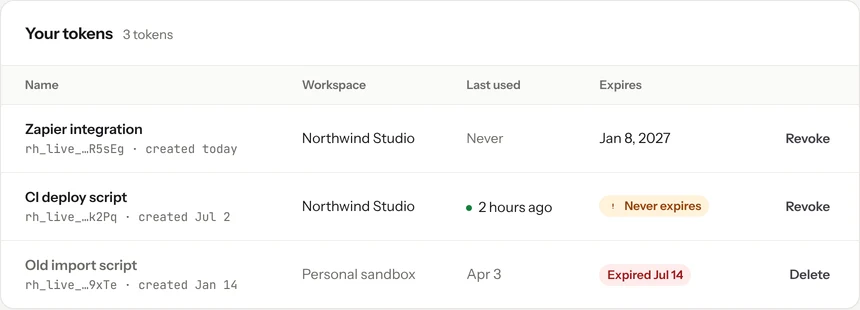
- Scoped to one workspace. A token acts inside one workspace. Changes made through the API, an AI assistant or a CSV import land in the same history as dashboard edits.
- Expiry, not forever. Each token carries a per-platform prefix and an expiry you choose, with a reminder a week before it runs out.
- Safe retries. Create requests accept an Idempotency-Key header, so a CI job that retries never creates a link twice.
- Redirects as code. The official Terraform provider manages redirects, migrations, branded links, QR codes and domains as code, and sends an Idempotency-Key on every create.
One per workspace. Full control, including deleting the workspace and transferring ownership.
Team settings, billing and members. Bulk invites, resend or revoke, inline role changes.
Creates, edits and deletes links, QR codes and domains. Every change lands in the history.
View only. Give auditors and agencies a window, not a key.
Core includes 3 team members; Pro includes unlimited members; on Enterprise, members are set by contract. Roles in detail →
Before / after
What changes when redirects leave the box in the corner
The same jobs, done on a self-run redirect server and on RedirHub.
Why teams choose RedirHub
5-star reviews on G2 and Trustpilot
Redirecting domain names with SSL is a huge pain, and I have to do it frequently, often at mass. Now it is a few clicks. It just works.
- domains live on HTTPS, certificates renewed automatically
- 300,000+

Zsolt Bikadi
CSO · Domain Science
The redirects work flawlessly, the dashboard is simple and easy to manage. The custom domain option was a great feature.
LG
The website has everything I need for redirect: URL redirect and shortlink. Easy interface to set up and manage my domains. Automatic SSL certificate setup. Best service on the market.
Henry
FAQ